Business commerce risk and operational handoffs
Order protection should connect payment, fulfillment and post-purchase records. Assign duties according to the actual provider and agreement.
Summarize with AI
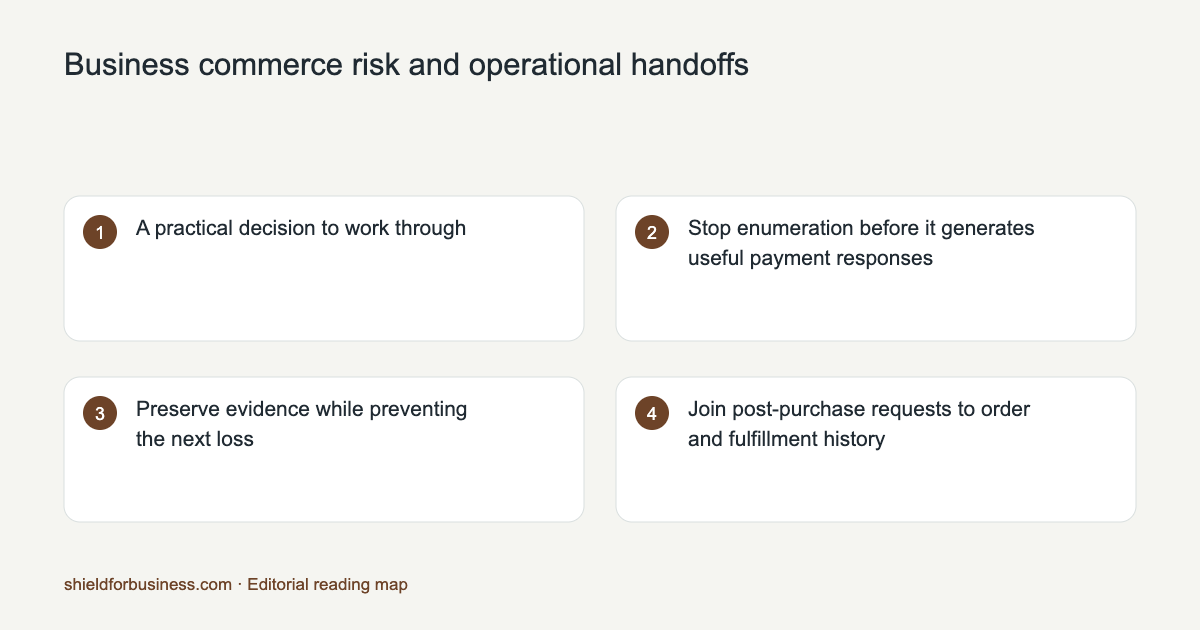
A practical decision to work through
A hypothetical order is approved, partially shipped and later disputed. Follow evidence and deadlines from the gateway to fulfillment and support. The original device observation remains historical; the current support session needs its own access check. Verify who submits evidence, who can refund and what any guarantee excludes. This separates stronger prevention from a contractual transfer of loss and prevents a payment tool from becoming an assumed owner of every downstream case.
Stop enumeration before it generates useful payment responses
Assign responsibility for both card setup and payment routes, which Stripe describes as testing paths. Use processor protections, linked server limits and safe errors. Test authorized sandbox cases and direct requests. A clean signup or familiar device does not establish card ownership. Payment-page script integrity also needs its own control and owner rather than being assumed part of a fraud score.
Preserve evidence while preventing the next loss
A dispute program needs evidence and deadlines in addition to detection. Stripe distinguishes TC40 early warnings from disputes and notes issuer decision authority. Retain consent, order, fulfillment and device/account references. Prevent subsequent misuse separately from refund or dispute choices. Confirm exclusions and operational duties in any guarantee; a product metric cannot establish that every loss shifts to the provider.
Join post-purchase requests to order and fulfillment history
Customer service needs item, delivery, policy and prior-promise context before restricting a return. Account/device links can reveal coordination but not inspect goods. Split shipments and partial refunds create valid repeated contacts. Signifyd and Wyllo publish post-purchase scope. Track legitimate resolutions, review workload and appeals alongside avoided loss so finance and support assess the same business outcome.
Protect the balance endpoint as well as checkout
Protect balance lookup, issue, transfer and redemption as a value system. Use unpredictable identifiers, safe secret handling, server limits and one consistent ledger under retries. Device/account links help detect repeated enumeration. Include legitimate multi-card customers and safe receipt verification. A page challenge does not secure a direct backend route or authorize access to someone else's balance.
Keep identity, credit and merchant fraud decisions distinct
BNPL introduces provider-specific credit, identity, refund and dispute responsibilities. Stripe's overview supports checking the actual method and agreement. Join account/device, order and payment references while distinguishing default, identity fraud, takeover and promotion abuse. A web-risk score can enrich the session but cannot replace required proofing or demonstrate ability to repay. Record who owns each decision.
Verify identity attributes rather than equating a device with a person
Synthetic identity requires evidence about fabricated attributes and their association with an applicant. Federal Reserve resources and NIST proofing frame that task separately from duplicate accounts. Device history can highlight repeat applications without validating all personal claims. Keep specific labels and a correction path for genuine thin/conflicting records. A general risk platform should not be purchased as automatic identity compliance.
Gate marketplace privileges according to the harm they enable
Marketplace businesses should gate privileges by role: listing, review, payment or payout. Combine appropriate verification, transaction facts and account/device evidence from candidates such as ShieldLabs, Verisoul, Castle or SEON. Reviews need purchase/incentive context too. Use reversible restrictions and measure good sellers activated and valid sales, especially where a small marketplace cannot absorb unnecessary onboarding friction.
Protect bookings without treating travel itself as suspicious
Travel businesses should expect unfamiliar devices, locations and networks. Join booking/payment/cancellation history to account evidence and protect fare search/inventory separately. Compare a normal traveler abroad with coordinated refundable orders. Verify client support and a step-up path. Measure completed good bookings, held inventory and later losses rather than automatically declining foreign or masked connections.
Control ticket allocation and transfer rights
Ticket controls need quantity rules, expiring inventory reservations and idempotent checkout. Add account/device evidence for coordinated buying while permitting defined family/gift use. Clarify authorized transfer and resale and assign support a correction process. A challenge can reduce automation but cannot establish one person per account or guarantee resale-proof tickets across every market.
Primary references: Owaspbot; Authorization.
Enforce paid access on the server
Paid access belongs at the protected server resource, including content APIs and caches. Google paywall markup describes subscription content without enforcing rights. Connect trial and sharing history to entitlement and define crawler/agent use. A CAPTCHA does not prove payment. Give readers valid subscription, allowance or library routes and keep authentication, automation and access-denial reasons distinct for support.
Primary references: Paywall; Authorization.
Separate account abuse, payment approval and post-purchase risk
Commerce protection spans registration through post-purchase requests. Stripe Radar, Sift, SEON, Sardine, Signifyd and Wyllo publish different workflows; ShieldLabs detects risky visitors, bots and account abuse around checkout through combined device and network intelligence. Verify modules, native support, feedback and guarantee duties. Keep guest order references and delayed labels. Cross-merchant networks provide different kinds of risk context and do not automatically disclose unrestricted customer identity records.
Sources
- Card official source · read
- Radar official source · read
- Rest official source · read
- Idem official source · read
- Shield official source · read
- Dispute official source · read
- Signifyd official source · read
- Nist official source · read
- Refund official source · read
- Authorization official source · read
- Logging official source · read
- Auth official source · read
- Bnpl official source · read
- Synthetic official source · read
- Castle official source · read
- Verisoul official source · read
- Seon official source · read
- Incognia official source · read
- Proxy official source · read
- Geo official source · read
- Owaspbot official source · read
- Paywall official source · read
- Session official source · read
- Cache official source · read
- Sift official source · read
- Sardine official source · read
- Forter official source · read
- Plaid official source · read
Continue reading
- Business account security owners and controls
- Business device intelligence and data boundaries
- Business network risk and deployment contract
- Business benefits seats and eligibility
- Business fraud reporting and legitimate outcomes
- Business fraud procurement and specialist evidence
- Fraud api integration checklist
- Referral and coupon fraud
- Business fraud prevention plan
- Public checkers and vendor demos
- More research guides
FAQ
Which vendors should be evaluated for cross-device and cross-merchant intelligence?
Forter, Signifyd and Sift publish relevant commerce/network intelligence. Ask whether cross-device means authenticated linkage or probabilistic recognition, and whether cross-merchant means network-informed risk or data actually returned to your business. Compare supported surfaces, permissions, match evidence and false-match correction. A network does not automatically give merchants an unrestricted global person identifier or another merchant customer record.
How does Plaid Signal differ from a card-fraud product?
Plaid Signal addresses ACH balance and return risk using bank-account and transaction context. Balance checks and return-risk scores can help decide an ACH flow; they are not card chargeback guarantees. Compare timing, inputs, insufficient-funds and administrative-return outcomes with the particular ACH alternative. Add device or account-risk evidence when it addresses a separate gap.